root@rootreap3r_
$ whoami --verbose [ok] senior ai security engineer · ts/sci · salt lake city, ut

Joshua Urianza.

RootReap3r · also spelled RootReaper / Root Reaper
Senior AI Security Engineer/AI Red Team/MCP & Agentic Security

I secure the layer where AI agents meet real tools and real data: MCP server security architecture, agentic threat modeling, and prompt-injection defense, with code-enforced permission boundaries instead of prompt-level promises. On the offensive side, 100+ reviewer-validated prompt-injection and jailbreak findings against live LLM products, and jailbreak research since mid-2022, before ChatGPT existed. Before AI security: 10+ years in cybersecurity, 7+ at the TS/SCI level across nuclear command and control, SAP/TEMPEST, and federal cloud. M.S. AI candidate at Georgia Tech.

TS/SCI · Active HTB COAE · #213 worldwide PWPE · Early adopter CompTIA SecAI+ · Beta cohort M.S. AI · Georgia Tech Jailbreak research since 2022
Joshua Urianza (RootReap3r), Senior AI Security Engineer
100+
validated prompt-injection & jailbreak findings on live LLM products
26
attack + guard modules shipped (Wraith 11 / Seraph 15), 420 tests
$147B
TS/SAP cloud program, full ATO across 10 NIST Rev 5 packages
<2 min
C2 dwell time, down from hours, via Splunk detections
2,730
adversary-informed assessments across four classification tiers
2022
first AI jailbreak research (Midjourney), before ChatGPT
scope of work

What I do

The question I keep answering for AI teams: what can this agent be tricked into doing, and what stops it at the code layer rather than the prompt layer?

ARCHITECTURE

MCP & agentic security architecture

Code-enforced tool-permission boundaries, governed MCP/A2A control planes, and threat models for agents that call tools, read untrusted documents, and talk to other agents. Multi-tenant isolation on AWS Bedrock Agents, Azure, and Kubernetes.

OFFENSE

AI red teaming

Direct, indirect, and cross-domain prompt injection, jailbreaks, MCP tool poisoning, schema injection, and cross-server privilege escalation. 100+ reviewer-validated findings against live client LLM products, scored against a structured red-team taxonomy.

DEFENSE

Adversarial evaluation & control verification

Harnesses that replace "the model said it was safe" with falsifiable pass/fail gates: canary extraction, PII and injection detectors, egress interceptors, and guard modules that ship with measured true- and false-positive rates.

FOUNDATION

Classified-environment security engineering

Lead ISSO for Sentinel and Nuclear Command & Control programs. Zero-days found by hand that enterprise tooling missed, ~2,500 controls authored, and full ATO on a $147B TS/SAP cloud program. Mapped to NIST 800-53 Rev 5, NIST AI RMF, MITRE ATLAS and ATT&CK.

essays & field notes

Writing

Firsthand research and engineering notes on AI security, newest first.

builds

Projects

Offense and defense built as a matched pair, plus governance tooling. Code on GitHub.

Wraith

AI red-team engagement harness

Python harness unifying AI red-team tradecraft across 11 attack modules: prompt injection and jailbreaks, MCP/RAG/A2A, adversarial-ML evasion, data poisoning, membership inference, model supply chain, and agent SSRF. Code-enforced scope gate, verbatim request/response evidence capture, scoring and report scaffolding, and an MCP server so agents can drive it.

11 attack modulesscope gateMCP server260 tests
Seraph

AI defense control verification library

Blue-team counterpart to Wraith: 15 detection and guard modules (indirect injection, taint-based exfiltration, MCP privilege boundaries, agent egress SSRF, supply-chain startup hooks, agent tampering with monitoring) mapped to a shared attack taxonomy, each shipping measured true- and false-positive rates. Includes a deployable egress interceptor validated end to end against Wraith's SSRF payloads.

15 guard modulesmeasured TP/FPegress interceptor160 tests
recon-sweep

Scope-gated agentic red-teaming harness

Replaces self-graded LLM safety scoring with deterministic pass/fail gates (canary extraction, PII regex, injection detection) and an advisory-only LLM judge calibrated against a golden set, aligned to NIST AI RMF MEASURE/MANAGE. The allowlist lives in code, so an injected prompt cannot widen scope. Technical breakdown →

NIST AI RMFcanary / PII gatesCIDR allowlist
RMF-AI-COPILOT

NIST 800-53 Rev 4 → Rev 5 migration pipeline

Generates SCTM, eMASS export, and POA&M items from SSP content, grounding every AI judgment against the full 1,189-entry Rev 5 catalog. Provider-agnostic (Anthropic, OpenAI, Bedrock GovCloud) and deployable air-gapped/NIPR with zero code changes.

NIST 800-53 Rev 5eMASS / SCTMair-gappedGovCloud
AI IR Tabletop

Adversarial LLM incident-response engine

An LLM plays a state-consistent threat actor across 23 scenarios and 9 MITRE-mapped APT profiles, with attacker and grader split across separate API passes and auto-generated after-action reports. Cuts exercise prep from weeks to hours.

23 scenarios9 APT profilesauto AAR
PHANTOM

AI-powered active defense & threat-hunting platform

Multi-agent active-defense platform with ML-based C2 beacon detection, passive attribution (geolocation, JA3, threat intel), confidence-gated response, and cryptographic chain-of-custody evidence. One-command FBI/CISA report generation in STIX 2.1.

ML beacon detectionJA3 / ASN attributionSTIX 2.1105 tests
track record
Sep 2026 — Present

Senior AI Security Engineer

Wilson Sonsini Goodrich & Rosati

AI security architecture and AI red teaming for the firm's enterprise AI platforms and agents.

Jul 2026 — Sep 2026

AI Red Teamer / AI Security Engineer (Contract)

Mercor | LinkedIn
  • Landed 100+ reviewer-validated prompt-injection and jailbreak findings (direct and cross-domain) across client LLM-integrated products, scored against a structured red-team taxonomy.
  • Surfaced MCP tool poisoning, schema injection, and cross-server privilege escalation by exploiting over-privileged servers across client AI tool infrastructure.
  • Built a multi-tenant AI chat widget embeddable on any site in under 30 minutes, with CORS allowlisting, prompt-injection screening, XSS-safe rendering, CSRF protection, and timing-safe auth.
Oct 2022 — Aug 2026

Senior Cybersecurity Engineer

Accenture Federal Services
  • Zero-day discovery & detection engineering: drove accreditation for a $147B TS/SAP cloud program by manually reverse-engineering zero-days missed by enterprise tooling, building an AI correlation engine (NVD/CVE/CNNVD) to automate triage, and engineering Splunk detections that cut C2 dwell time from hours to under 2 minutes, securing full ATO across 10 NIST Rev 5 control packages.
  • Supply-chain security: built a risk-correlation tool cross-referencing NVD and ExploitDB against asset versions to surface unpatched vulnerabilities, with open-source/GitHub sweeps and foreign-influence and vendor-provenance checks on hardware, software, and AI components.
  • Threat & risk assessment: ran 2,730 adversary-informed assessments across unclassified, Secret, and TS/SAP environments, correlating 524 vulnerability scans and 476 audits through offensive-security expertise and exploit research.
  • Incident response & scenarios: architected the IR plan and designed 16 quarterly adversarial scenarios spanning four classification tiers, authoring each from threat model through after-action report.
  • Compliance & governance: authored accreditation packages (~2,500 controls, SCTMs, SSPs) as Lead ISSO for Sentinel and Nuclear Command & Control programs.
Oct 2020 — Oct 2022

Security Program Manager

DS&S
  • Personnel & insider threat: directed personnel security and insider threat for 2,350+ AFNWC personnel with TS/SAP access, including counterintelligence vetting, clearance adjudication, and need-to-know validation for Restricted Data; managed direct reports, hiring, and performance reviews.
  • Physical & nuclear C2 security: owned security for $41M+ in SAP/TEMPEST facilities and networks carrying NC2 design data and DOE Restricted Data, running adversarial assessments across every control layer with zero attributable incidents.
  • Customer recognition (2021): formally recognized after an ICBM Systems Directorate Security Support PMR, where the government customer cited outstanding performance and a new badging-system plan delivered to the Deputy Director.
Mar 2020 — Oct 2020

Cyber Automation Lead

Sebastian Tech Solutions (DISA)
  • Built SOAR and PowerShell/Python automation for account remediation, access provisioning, and IR triage, cutting escalation decisions on compromise cases from minutes to seconds across DISA, White House, Pentagon, and 7th Fleet environments.
Apr 2018 — Mar 2019

Cyber Investigations Lead

Netflix
  • Led response to a credential-stuffing campaign compromising 900+ accounts, correlating device, IP, geolocation, and VPN signals to restore 100% of accounts to their owners.
Aug 2015 — Apr 2018

Incident Response Lead

The Results Company
  • Advanced from help desk analyst to IR Lead, resolving 10,264 tickets and coordinating a multi-person IR team while sustaining a 96% stakeholder satisfaction score.
Jan 2017 — Jan 2023

Weapons Director

Air National Guard
  • Directed up to 30 aircraft ($2B+ in F-22/F-35/F-15/F-18 assets) across 100+ sorties in live coalition exercises including Red Flag-Alaska and Northern Lightning, on full-time orders Mar 2019 to Mar 2020. Completed Teal Rope Initial Training (81st Training Wing SAPR Office, Oct 2018).
Why a Weapons Director makes a good red teamer

A Weapons Director sits in an Air Operations Center or Control and Reporting Center, watching a live radar picture and directing fighter aircraft in real time: sorting real threats from noise, prioritizing which contact gets worked first, and issuing short, unambiguous instructions to pilots who rely on your read because they can't see what you can see. It's high-tempo decision-making under incomplete information, inside a strict rules-of-engagement framework, where a wrong call has immediate consequences.

That maps closely to AI red teaming and incident response: triaging a flood of findings, deciding what's a real threat versus noise, working inside an explicit scope boundary, and communicating clearly and fast when the picture is incomplete.

A film scene, not real footage, but the closest illustration of what that decision tempo feels like.

Also fiction, but a reasonable stand-in for the operations floor a Weapons Director works from.

credentials

Certifications

Click a node to see the certificate. Gold = completed, purple = in progress.

Select a node

Click any certification above to view the certificate, domain alignment, rarity, and offensive/defensive weighting.

Also: Microsoft Certified Azure AI Fundamentals. Choosing your own next cert? See the full interactive security certification roadmap, a vendor-neutral breakdown by rarity, domain, and offensive vs. defensive focus.

background

Education & awards

In progress

M.S. Artificial Intelligence · Georgia Institute of Technology

Part-time. Research: adversarial robustness and red teaming of LLM agentic systems.

Completed

B.A.S. Cyber Operations, Defense & Forensics · University of Arizona

NSA Center of Academic Excellence in Cyber Operations. Malware reverse engineering and digital forensics.

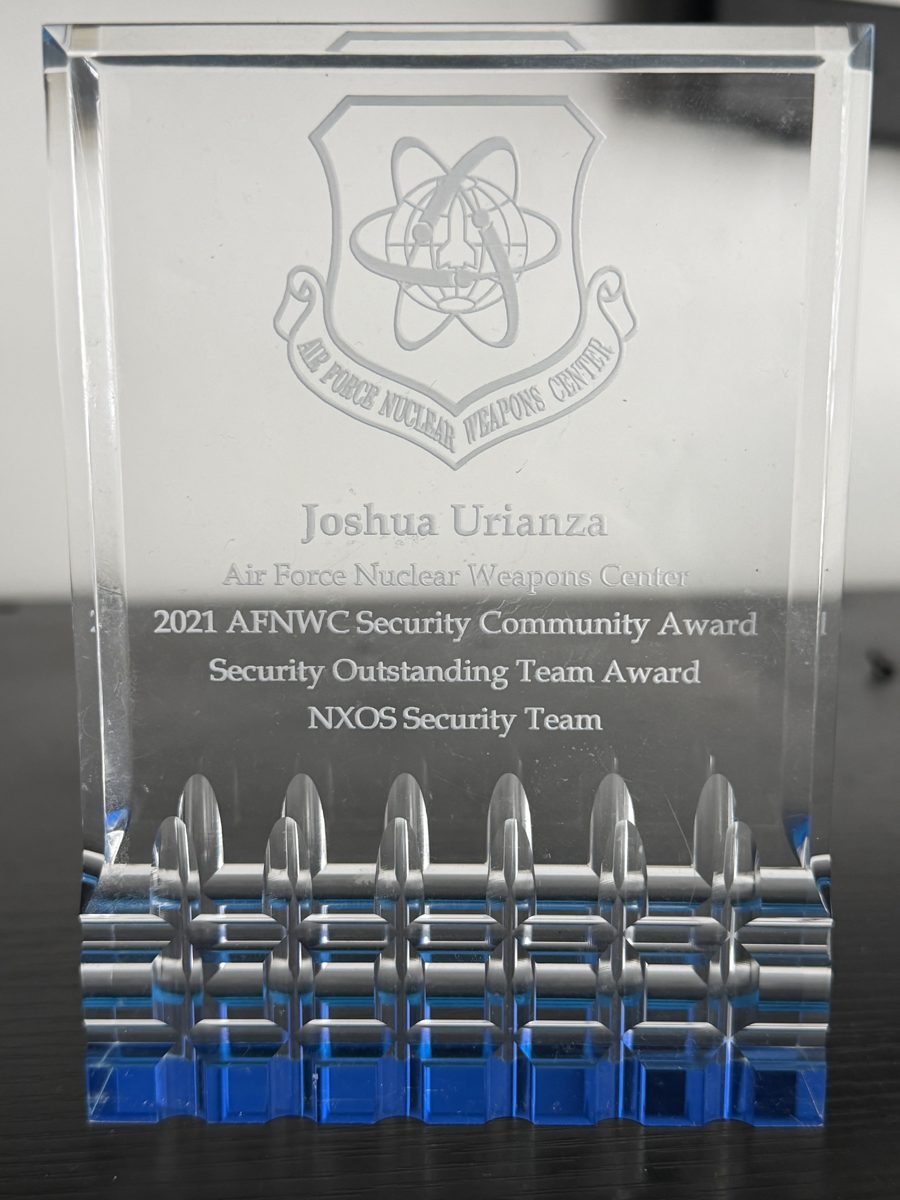
2021

Security Team of the Year · Air Force Nuclear Weapons Center

AFNWC Security Community Award, Security Outstanding Team Award, NXOS Security Team. Also: Minuteman III Personnel Award and ICBM Personnel Award.

2021 AFNWC Security Community Award crystal plaque presented to Joshua Urianza, NXOS Security Team
2021 AFNWC Security Community Award, NXOS Security Team.
stack

Skills & frameworks

AI security
MCP security architecture, prompt injection (direct, indirect, XPIA), jailbreaking, tool poisoning, agentic threat modeling, LLM red teaming, RAG security, AI incident containment
Frameworks
OWASP Top 10 (LLM, MCP, API, Web), MITRE ATLAS and ATT&CK, NIST AI RMF, NIST 800-53 Rev 5, RMF/ATO
Cloud & platform
AWS (IAM, Bedrock Agents), Azure (Sentinel, Entra, Defender for Cloud, Purview), GCP, Kubernetes (RBAC, admission control), Terraform, multi-tenant isolation
Detection & telemetry
Splunk, Microsoft Sentinel, OpenTelemetry (GenAI semantic conventions), CloudWatch, Sysmon, Zeek, STIX 2.1
Offensive tooling
Metasploit, Cobalt Strike / Sliver, Mimikatz / BloodHound, ACAS, SOAR
Languages
Python, Go, Bash, PowerShell
off the clock

Music & wrestling

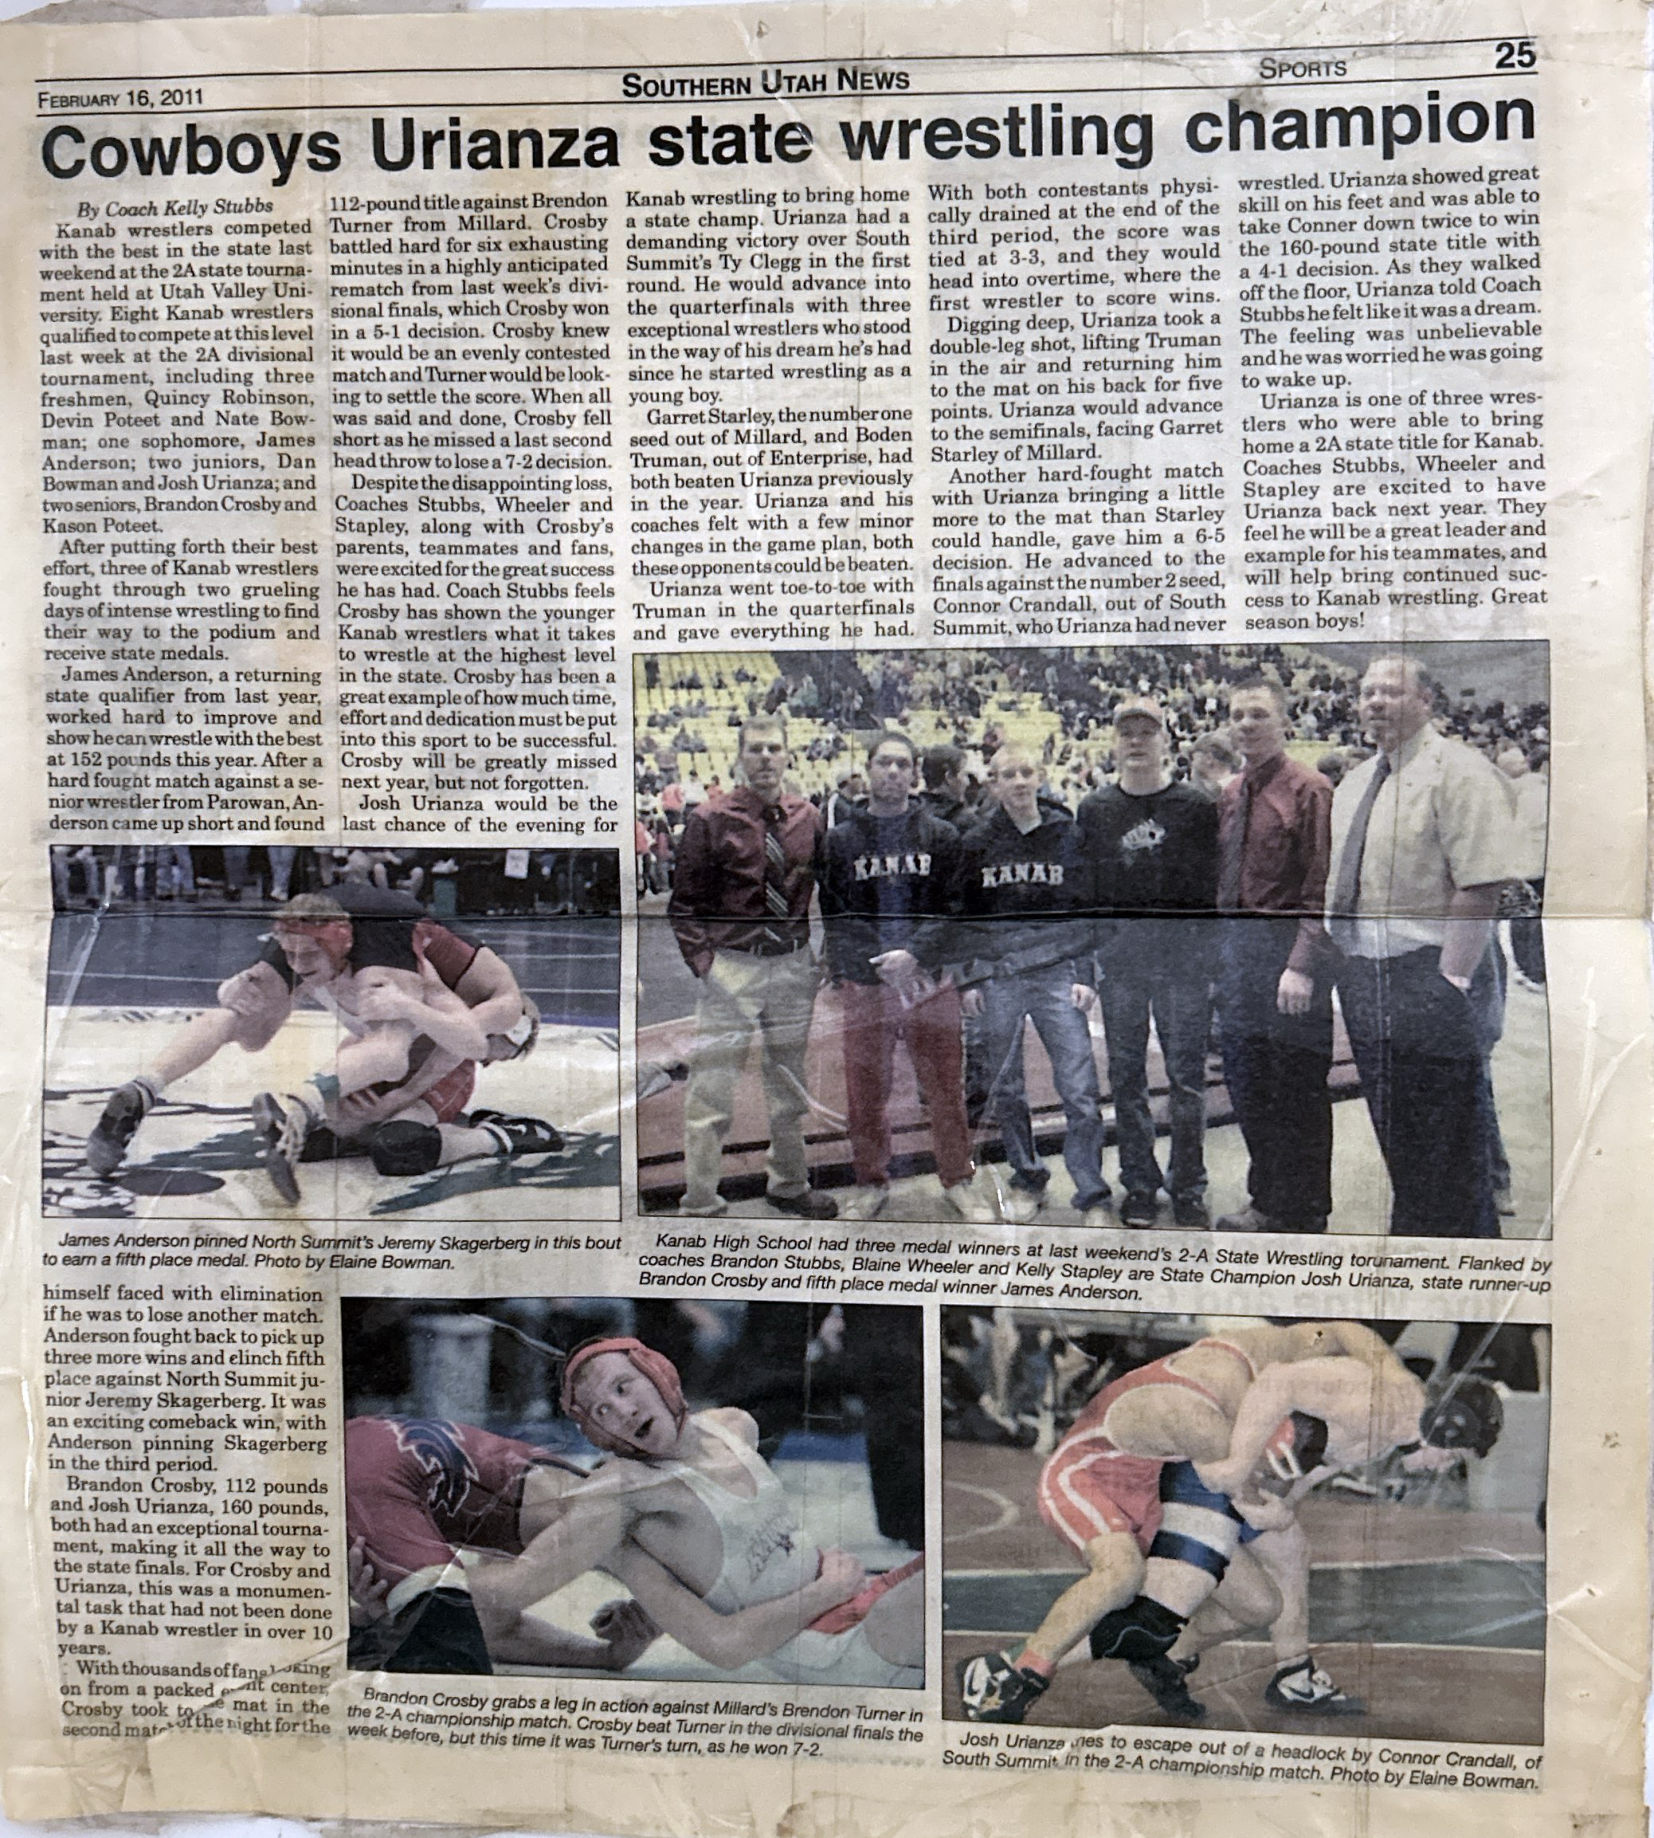
Southern Utah News sports page from February 2011 covering the Utah 2A state wrestling championship

2011 Utah 2A state wrestling champion

160 lbs, Kanab High School. These days I'm on the other side of the mat, coaching youth wrestling.

Round-by-round and the newspaper clipping →
reach out

Contact

Open to conversations about AI security architecture, agentic threat modeling, MCP security, and AI red teaming.

$ cat contact.txt
email[email protected]
linkedinlinkedin.com/in/joshua-urianza
phone385-985-8433
githubgithub.com/RootReap3r
locationSalt Lake City, UT
résuméJoshua-Urianza-Resume.pdf